
Codex CLI Auto Mode and YOLO: Commands, Approvals and Sandbox
By CodeAgentSwarm · Updated October 5, 2026
How to run Codex CLI in Auto Mode
The OpenAI approvals documentation calls this combination the Auto preset: workspace-write with on-request approvals. Codex can do routine work within its permissions and request approval when it needs to go beyond them. To enable this Auto Mode configuration explicitly, run:
codex --sandbox workspace-write --ask-for-approval on-request "Review the project and run its tests"For a run without approval prompts, keep the sandbox and use --ask-for-approval never. Blocked operations fail instead of prompting for permission.
codex --sandbox workspace-write --ask-for-approval never "Run the existing tests"The command codex --yolo also bypasses the sandbox. Reserve it for an externally isolated environment without production credentials or data. A Git branch does not provide that isolation.
If you need to see what Codex is doing, the Codex GUI puts several conversations in one window. To divide work between agents, follow the guide to multiple Codex sessions.
What approvals, sandboxing and --full-auto do
When Codex asks
| Configuration | Behavior |
|---|---|
| --sandbox workspace-write -a on-request | Works within configured boundaries and can request permission to go beyond them. |
| --sandbox workspace-write -a never | Keeps the boundaries and does not request escalation; blocked operations fail. |
| --yolo | Alias for --dangerously-bypass-approvals-and-sandbox. Bypasses both protections. |
| --full-auto | Legacy flag. Availability depends on the version and subcommand. |
In Codex CLI 0.156.0, we checked that codex --full-auto --help rejects the argument while codex --yolo --help accepts it. The official codex exec reference still describes --full-auto as deprecated compatibility. Use explicit options and check the help for the command you intend to run.
codex --version
codex --help
codex exec --help
What the sandbox restricts
The sandbox limits resources the process can access. Approval policy controls requests to act beyond those boundaries. Disabling prompts alone does not grant full access. workspace-write permits changes within the workspace, which can include deleting files there. Keep a backup of important work.
Sources checked September 25, 2026: OpenAI command reference; sandbox documentation.
Risks that remain
- Writable files can be overwritten or deleted even inside a sandbox.
- Accessible credentials, services and paths determine what a command can reach.
- A branch separates Git history; it does not isolate processes, secrets or external services.
- AGENTS.md guides the agent; it does not replace access restrictions.
How to supervise Codex in CodeAgentSwarm
1. Start with bounded permissions
Open the project and select Codex. You can use Chat or the terminal. Check that session’s permission mode before sending the task. In the terminal, use the Codex options explained at the start of this guide.
2. Review each session’s work
Open another session for an independent task, review project changes and consult saved conversations. If both tasks will edit the same files, use worktrees to separate working copies.
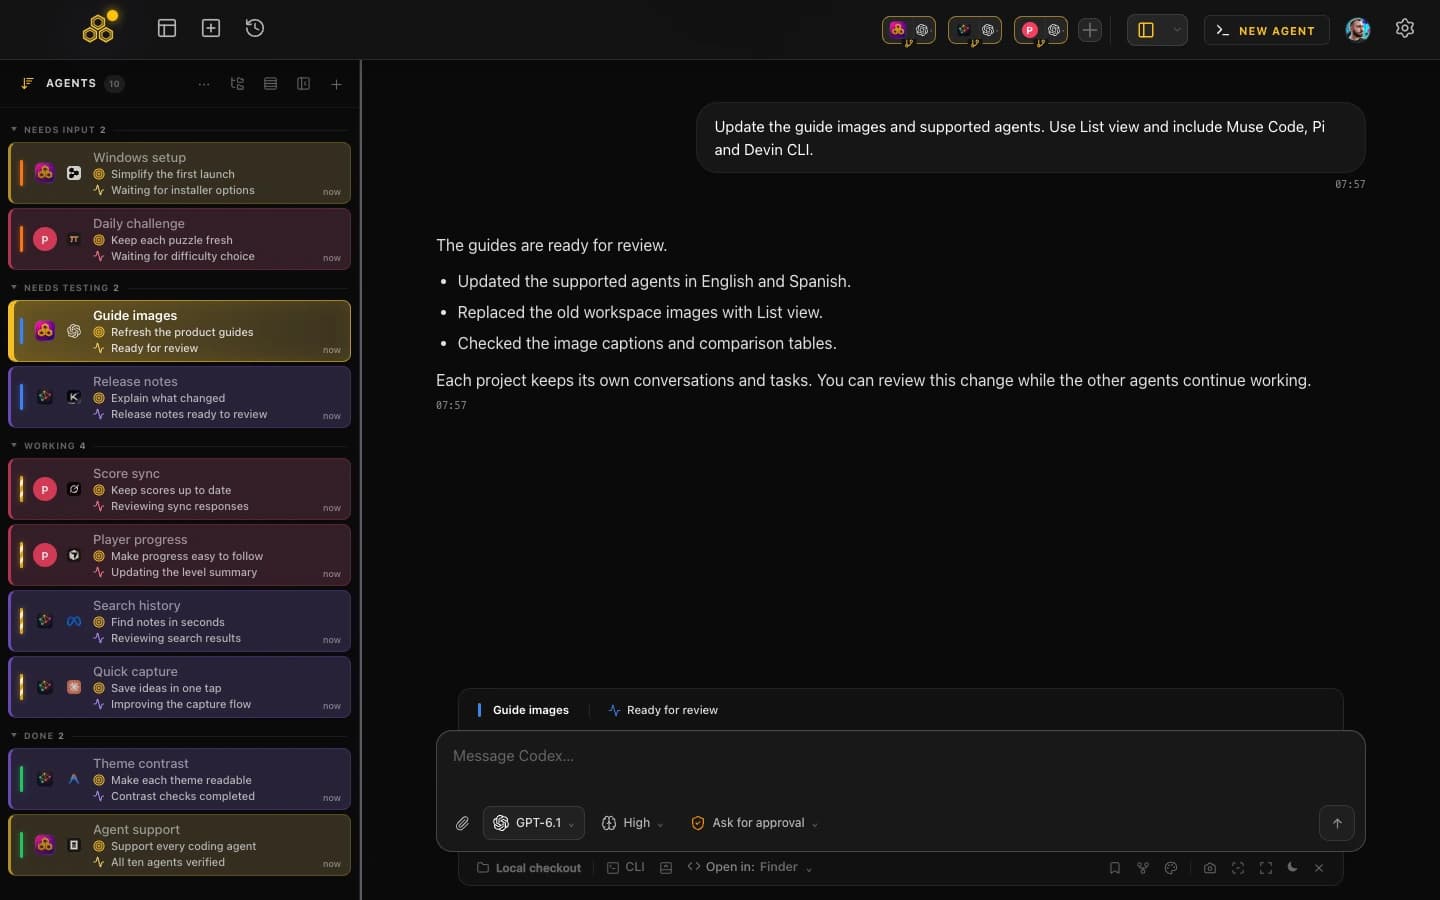
3. Check what Turbo Mode enables
Turbo Mode in the Codex terminal uses --dangerously-bypass-approvals-and-sandbox. Do not enable it expecting CodeAgentSwarm to automatically block a push or deletion. Visual supervision does not restore a disabled sandbox.
The Codex GUI guide explains how to open the app, sign in and review work. CodeAgentSwarm is a separate download from Codex and uses your provider account.
Before leaving a task running
- Save unfinished work and check git status before starting.
- Choose a specific project and task. Keep production credentials out of the working environment.
- Keep the sandbox enabled and check the session’s effective permissions.
- Review the diff and run tests before merging or publishing changes.
FAQ
What is Codex Auto Mode, and how do I enable it?
Codex Auto Mode combines the workspace-write sandbox with on-request approvals. Run codex --sandbox workspace-write --ask-for-approval on-request. Codex can work within the configured permissions and request additional access when needed. Auto-approve does not have to mean YOLO: --yolo bypasses both approvals and the sandbox.
Is there a codex --yolo flag?
Yes. --yolo is an alias for --dangerously-bypass-approvals-and-sandbox. It bypasses approvals and the sandbox. It is intended for externally isolated environments.
What does --full-auto do in Codex?
It is a legacy flag. The codex exec reference marks it as deprecated compatibility; the interactive command in Codex CLI 0.156.0 that we checked rejects it. Use --sandbox workspace-write and choose approval policy explicitly.
How do I run Codex without prompts while keeping the sandbox?
Use codex --sandbox workspace-write --ask-for-approval never. Codex will not request escalation; blocked operations fail. Files that are writable remain exposed to changes and deletion.
What is the difference between the sandbox and approvals?
The sandbox limits accessible resources. Approval policy controls when Codex asks to extend that access. You can keep the sandbox even when you do not want prompts.
Does CodeAgentSwarm Turbo Mode block dangerous Codex commands?
Do not assume that it does. Turbo Mode in the Codex terminal uses the flag that bypasses approvals and sandboxing. Keep normal permissions when you need those restrictions.
How do I supervise multiple Codex sessions?
CodeAgentSwarm provides independent sessions, conversation history and project change review in an app for macOS, Windows and Linux. Configure permissions for each session and use worktrees when you need separate working files.